Understanding SHA-256: The Core Cryptographic Function Behind bitcoin
At the heart of bitcoin’s security framework lies the SHA-256 hashing algorithm, a cryptographic function that ensures the integrity and security of the blockchain. Unlike symmetric encryption, which uses the same key for encryption and decryption, SHA-256 is a one-way cryptographic hash function, meaning it’s extremely tough, if not impractical, to reverse-engineer the input data from its hash output. This characteristic makes SHA-256 an invaluable tool in securing data transactions within the bitcoin network.
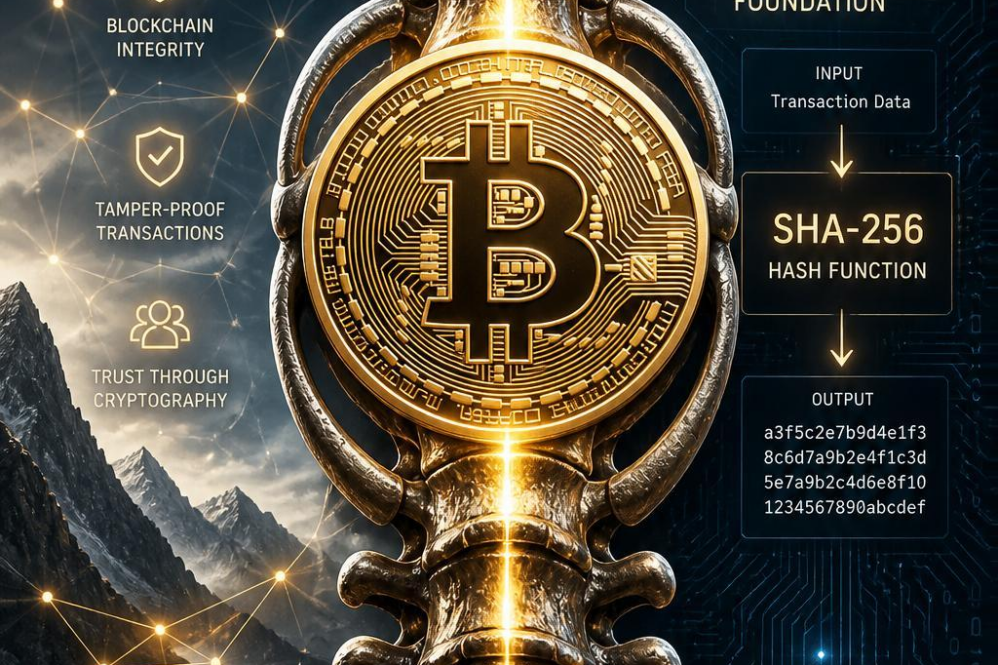
The process begins when a new transaction is validated and needs to be added to the blockchain. The transaction details, including sender and receiver addresses, amounts, and timestamps, are combined and fed into the SHA-256 algorithm. This input, often known as the transaction data, is transformed through a series of complex calculations into a 256-bit hexadecimal string, or hash. Each hash, despite being unique and non-reversible, can be generated quickly, ensuring that transactions can proceed without delays, yet maintaining robust security against tampering or manipulation.
A critical component of the SHA-256 function is its avalanche effect, which ensures that even a minor change in the transaction data produces an entirely different hash. This attribute is crucial in maintaining the trust and reliability of the blockchain. As an example, if a hacker attempts to alter a transaction’s details, the resulting hash would change dramatically, making it immediately apparent that the transaction has been tampered with. This inherent property of SHA-256 makes it virtually impossible for malicious actors to manipulate transaction records without being detected.
The Role of Hash Functions in Securing bitcoin Transactions
Hash functions are fundamental to the security architecture of bitcoin, playing a pivotal role in ensuring the integrity and security of transactions.In the context of bitcoin, the SHA-256 algorithm is used extensively to create unique digital fingerprints for every block and transaction on the blockchain. These fingerprints, known as hashes, are fixed-length codes that are nearly impossible to reverse-engineer back to the original data, offering a powerful layer of security. Thanks to this feature, SHA-256 enables miners to verify the legitimacy of transactions and create new blocks on the blockchain by solving complex mathematical puzzles.
The mechanism through which SHA-256 ensures security is both elegant and robust. Each transaction included in a block is hashed along with the hash of the previous block, forming a chain of transactions. This chaining process is critical because it means altering any single transaction requires recomputing all subsequent hashes, a task requiring an immense amount of computational power. The complexity of this computational challenge makes it highly unlikely that any malicious actor can modify transaction data without detection. Hence, every alteration to the blockchain would leave a trace, making it clear and tamper-evident.
To illustrate the hash generation process in bitcoin, consider the following table that shows how a simple string is transformed into a SHA-256 hash:
| Input String | SHA-256 Hash |
|---|---|
| Hello World | 8d10bf5ee299e7c75e9c41e2c937f531e6ca58264c2da0b54b0265b31d017a7b |
| bitcoin Transaction | 49f9e97c05f9c5ec93e8d7aae338a7d1a3e09c0aa095ce44a42ee6786a832e3f |
This table demonstrates the transformative power of SHA-256, showing how varied inputs produce unique and seemingly random hash outputs. This characteristic reinforces the security of the blockchain, as each transaction’s hash is unique and unpredictable, making it near impossible to manipulate without detection.
How SHA-256 Miners Contribute to Blockchain Security and Network Integrity
The heart of bitcoin’s security lies in the SHA-256 mining process, which acts as a digital fortress against fraudulent activities. Miners play a crucial role in validating transactions and creating new blocks, but their impact extends far beyond these immediate tasks. They contribute to the blockchain’s integrity by solving complex mathematical puzzles that are designed to be computationally intensive yet verifiable. This process is what secures the ledger against double-spending and other forms of tampering.
SHA-256 miners enhance the network’s resilience by increasing the difficulty of modifying past transactions-a property known as immutability. Every block in the blockchain includes a hash not only of its own data but also of the previous block’s hash, creating a chain where altering one block would require recalculating the hashes of all subsequent blocks. This makes any attempt to defraud the system exceedingly difficult, as the computational effort required would be enormous and highly visible to the network. the decentralized nature of the network, with miners scattered worldwide, means that any attempt to manipulate the blockchain would be met with resistance from the collective computing power of the community.
To better understand the miners’ role, consider a simplified comparison of blockchains secured by different hashing algorithms. bitcoin,relying on SHA-256,and Ethereum,which historically used Keccak-256 (later transitioning to Ethash for Proof of Work),have distinct approaches to securing their networks. As shown in the table below,both systems ensure security through proof of work,but SHA-256 requires more specialized and costly hardware,which deters malicious actors by raising the economic barrier to entry. This contributes to a higher level of security and protection against attacks for bitcoin.
| Blockchain | Hashing Algorithm | Primary Security Feature |
|---|---|---|
| bitcoin | SHA-256 | High difficulty, costly hardware |
| Ethereum (old PoW) | Keccak-256 | Cost-effective hardware |
Evaluating the Strength and Limitations of SHA-256 in Cryptocurrency Security
SHA-256, a cryptographic hash function, stands as the cornerstone of security for bitcoin and numerous other cryptocurrencies. This function’s primary purpose is to take an input-often a block of data or a transaction-and produce a fixed-size string of bytes. This output is nearly impossible to reverse-engineer or predict, making it an invaluable tool for securing data integrity and preventing fraudulent activities in the blockchain environment.What separates SHA-256 from its predecessors is its resistance to a wide array of attacks, particularly brute force and collision attacks, which ensures that even if attackers gain control over an extensive network, they will struggle to undermine the integrity of the transactions recorded within the blockchain.
However, SHA-256 is not without its limitations.One major drawback is the computational intensity involved in generating hash functions.The process of hashing each transaction,especially for larger blockchains with a high volume of transactions,demands meaningful computing power. This can lead to higher electricity costs and environmental concerns for miners. Moreover, as cryptographic techniques evolve, so do the methods of attack. While SHA-256 remains robust, the possibility of future algorithms breaking down its security barriers cannot be entirely dismissed.For instance, advances in quantum computing pose a significant threat to current cryptographic methods, including SHA-256.
Another limitation arises from the sheer scale of blockchain networks. As more transactions are added, the size of the blockchain grows, potentially slowing down the verification process and complicating the distribution of the ledger across the network. This can hinder the efficiency and scalability of the system beyond its current capabilities.the decentralized nature of cryptocurrencies means that network security often relies heavily on the collective effort of miners,who provide the necessary computational power to verify transactions. This dependency on a vast network of participants can be a double-edged sword,as a malicious attacker could potentially amass enough power to launch a 51% attack,where control over the network’s majority hash rate allows manipulation of the blockchain.
| Feature | Pros | Cons |
|---|---|---|
| Security Against Attacks | High resistance to current attack methods | Increased vulnerability to future quantum computing advances |
| Computational Power | Ensures robustness through demanding hash computations | High electricity consumption and environmental impact |
| Scalability | Secure and reliable transaction verification | Slowdowns and inefficiencies as network size increases |
Strategic Considerations for Future Proofing bitcoin Against Quantum Threats
One key consideration for future-proofing bitcoin against quantum threats is the advancement and integration of post-quantum cryptography. This involves transitioning to algorithms that quantum computers cannot efficiently break. Quantum-resistant techniques need to be carefully selected and tested to ensure they maintain a robust level of security while also preserving the efficiency and decentralization that bitcoin values so highly. Efforts are currently underway to identify and standardize these new security measures.
To effectively implement post-quantum solutions, stakeholders must look beyond pure technical aspects. Strategic planning should include policy considerations, educational outreachand community engagement. For example, developers need to understand the implications of quantum-resistant algorithms and how to integrate them into existing systems. regulatory bodies should be proactive in updating guidelines to accommodate the new cryptographic standards. Here’s a brief overview of some strategic areas to focus on:
| Strategic Area | Key Actions |
|---|---|
| Policy and Regulation | Develop guidelines for post-quantum cryptography adoption |
| Education | Provide resources and training for developers |
| Community Engagement | Promote awareness and collaboration within the bitcoin ecosystem |